DPO Radio
 ComplianceOne
A Vietnam-first GRC platform that converts privacy, data, AI, cybersecurity and sector requirements into structured workflows, controlled evidence and regulator-ready dossiers, accelerated by Forseti AI.
Compliance Modules
Regulatory Packs
Operational AI Workflows
Work Automation
Enterprise Users
Compliance cannot be managed through policies, spreadsheets and disconnected emails.
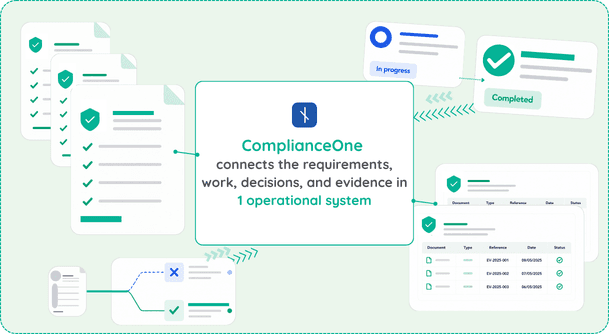
HOW COMPLIANCEONE WORKS
Installed regulatory frameworks define the obligations. ComplianceOne turns them into assigned approvals and exportable evidence as the work happens.
CORE PLATFORM CAPABILITIES
Platform administration, onboarding, dashboards, AI-assisted guidance and user management.
Consent, data mapping, classification, ROPA, data subjects and rights requests.
Vendor records, processor oversight, contracts, evidence and deletion controls.
DPIAs, cross-border transfer assessments, risk reviews and mitigation tracking.
Incident response, breach timelines, notifications and authority-ready records.
Ownership, deadlines, escalation, program governance and access accountability.
FORSETI AI
Automate up to 90% of structured compliance work, while keeping review, approval and decision-making under human control.
Grounded in your records & installed regulatory frameworks.
Drafts DPIAs, CbTIAs, ROPA, authority responses & remediation plans.
Supports compliance, legal, privacy, vendor, risk & audit workflows.
Provides citations for regulatory conclusions.
Requires human approval before records or evidence are changed.
Preserves complete audit lineage.
Pre-configured frameworks and local guidance to keep compliance work structured, current and audit-ready.
Your Compliance Foundation
CORE VIETNAM FRAMEWORKS
EVIDENCE & REGULATOR READINESS
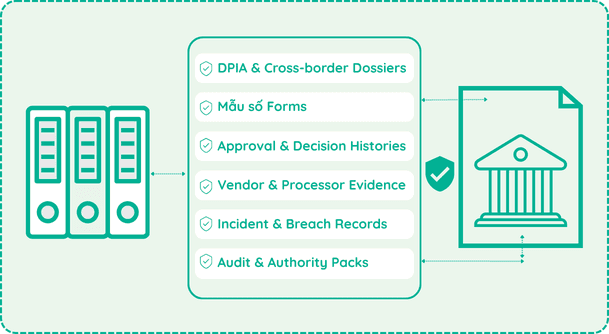
Build the evidence trail as compliance work happens. ComplianceOne captures actions, approvals and decisions in structured records, ready for audit, review or regulatory submission.
DEPLOYMENT AND DATA CONTROL
ComplianceOne governs the organization’s obligations and evidence. AesirX Privacy Scanner, CMP, Analytics, and First-Party Server extend that control into websites and digital services, connecting actual data collection and consent enforcement with internal governance records.
Combine for full impact and save 28%!
ENTERPRISE USE CASES
ComplianceOne supports privacy, regulatory, AI and third-party governance across complex organizations. Build the workflows you need now, then extend the same system across entities, frameworks and client programs without fragmenting ownership or evidence.
AesirX ComplianceOne is a Governance, Risk and Compliance (GRC) platform that helps organisations turn regulatory requirements into structured compliance operations. It connects obligations with registers, assessments, workflows, tasks, approvals and evidence across privacy, data governance, risk, vendors, incidents and other regulatory activities.
ComplianceOne supports operational regulatory packs for Vietnam's privacy, data, cybersecurity, AI, telecommunications, e-commerce, digital transformation and related requirements. Organisations can manage overlapping regulatory obligations while keeping the relevant workflows, responsibilities and evidence connected to each framework.
ComplianceOne connects regulatory obligations with structured workflows, responsibilities, approvals and evidence. As compliance work is completed, the platform creates a traceable record of actions and decisions that can support audits, regulatory reviews and the preparation of structured evidence and regulatory dossiers.
Forseti AI is the auditable legal and compliance advisor built into ComplianceOne. It works with installed regulatory packs and organisational compliance records to support activities such as assessments, regulatory drafting, vendor reviews, remediation and audit preparation. Human approval remains part of controlled actions, with grounding, citations and audit lineage supporting review and accountability.
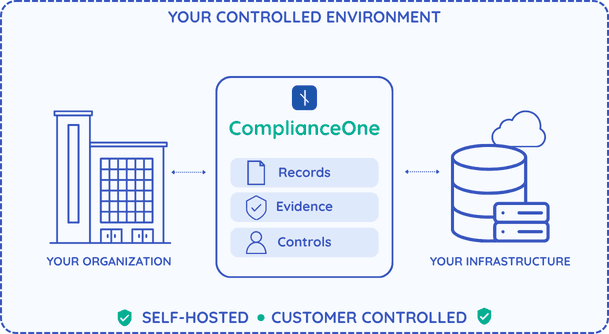
Yes. ComplianceOne is designed as a self-hosted GRC platform, allowing organisations to maintain control over where their compliance records and evidence are stored. Role-based access, accountability controls and audit capabilities support organisations managing sensitive regulatory and compliance information.

Discuss your compliance requirements and see the ComplianceOne capabilities most relevant to your organization.

Test ComplianceOne with your own requirements, workflows and team in a guided setup.

The evolution of Aesir is Aesir +  (the Norse symbol for Necessity)"Needed in order to achieve a particular result"
♥Join the AesirX Privacy Newsletter. Stay Informed. Stay Compliant.